By “cyber prints,” this could mean things like device/browser fingerprints, malware fingerprints, network traffic patterns, writing style, code style, command timing, infrastructure reuse, or attacker tactics.
How AI Estimates Probabilities
AI can compare those traces against known patterns and estimate probabilities such as:
- “Likely Windows host, 80–90% confidence.”
- “Possibly same operator as prior incident, moderate confidence.”
- “Traffic pattern resembles bot automation more than human browsing.”
- “Malware shares code lineage with family X, but attribution to actor Y is weak.”
The Bayesian Approach
The basic idea is Bayesian: new evidence updates an earlier probability.
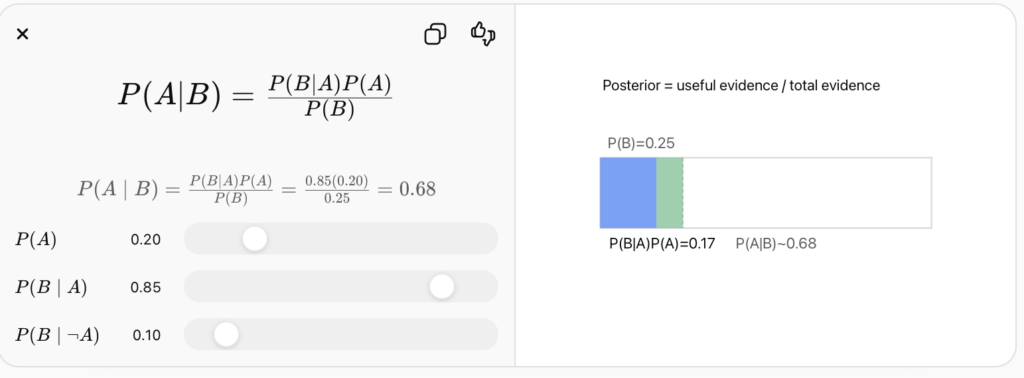
Posterior = useful evidence / total evidence
The Power of Correlation
Where AI helps most is in correlation across many weak signals: IP history, TLS fingerprints, user-agent quirks, compile timestamps, language artifacts, reused domains, malware strings, behavior sequences, keyboard timing, and TTPs.
Any one clue may be easy to fake, but many clues together can narrow the range.
The Big Caution: Evidence Manipulation
Cyber evidence is highly manipulable. Attackers can use VPNs, proxies, stolen devices, spoofed metadata, copied malware, false-flag infrastructure, or AI-generated behavior to imitate another actor.
Modern research even warns that AI-driven adversary emulation can weaken traditional TTP-based attribution because agents can mimic known threat groups.
Conclusion & Safe Forensic Framing
AI can reduce uncertainty about cyber-print attributes, but it should express results as probabilities with confidence levels, not as absolute identification. It is better for “this looks like X” than “this was definitely person Y.”
A safe forensic framing is:
- artifact → account/device → operator → organization/state
So Cyber Print probabilities using attributes can be established with AI, which in turn provides leads, which can move investigations forward.